
Open and transparent
Apache-2.0 licensed. No connections to project servers by default, and nothing is collected or reported.
DNS and NAT traversal, reverse proxy and HTTPS certificates, WAF and intrusion prevention, single sign-on and file sharing: everything your home network and servers need at the edge, managed from one console. Run it on a NAS, a soft router or a cloud server and set it all up in your browser.
Platforms and integrations
Every point below is a feature you can use today.
Apache-2.0 licensed. No connections to project servers by default, and nothing is collected or reported.
DDNS, traversal, reverse proxy, certificates, WAF, networking, Docker and file services in one console.
WAF, intrusion bans, IP and country rules, single sign-on and two-factor auth, configured per site.
Sign-ins, config changes and access to sensitive content are recorded, so you can see who did what and when.
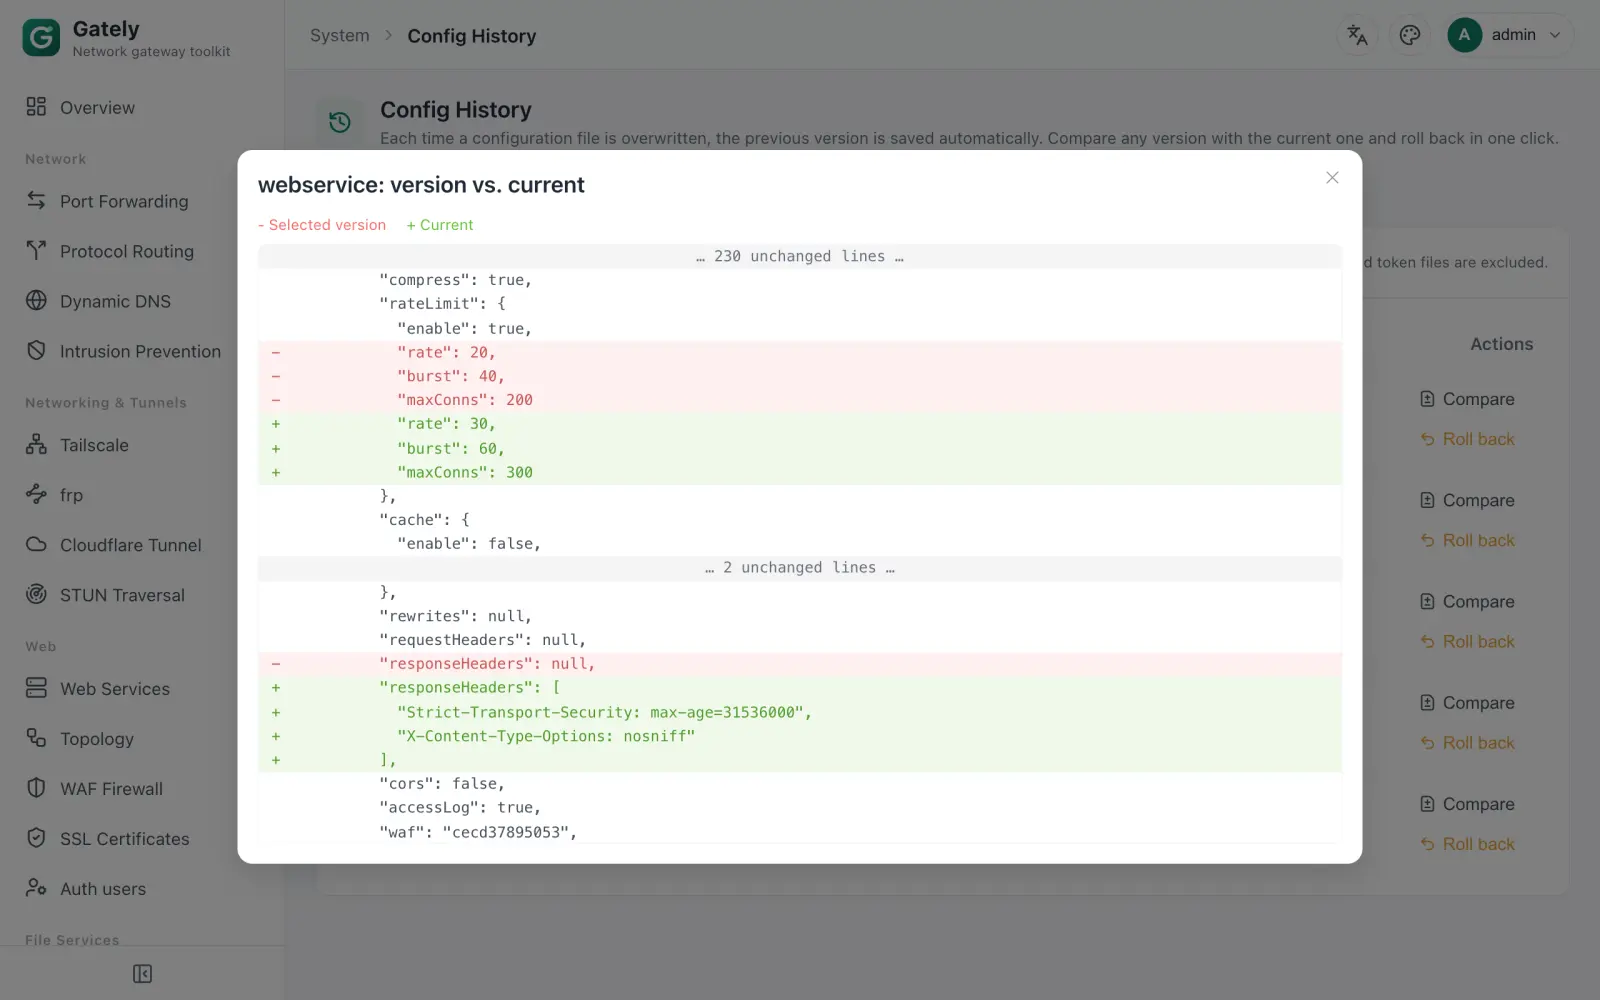
Every change keeps the previous version. Compare the diff and restore it in one click.
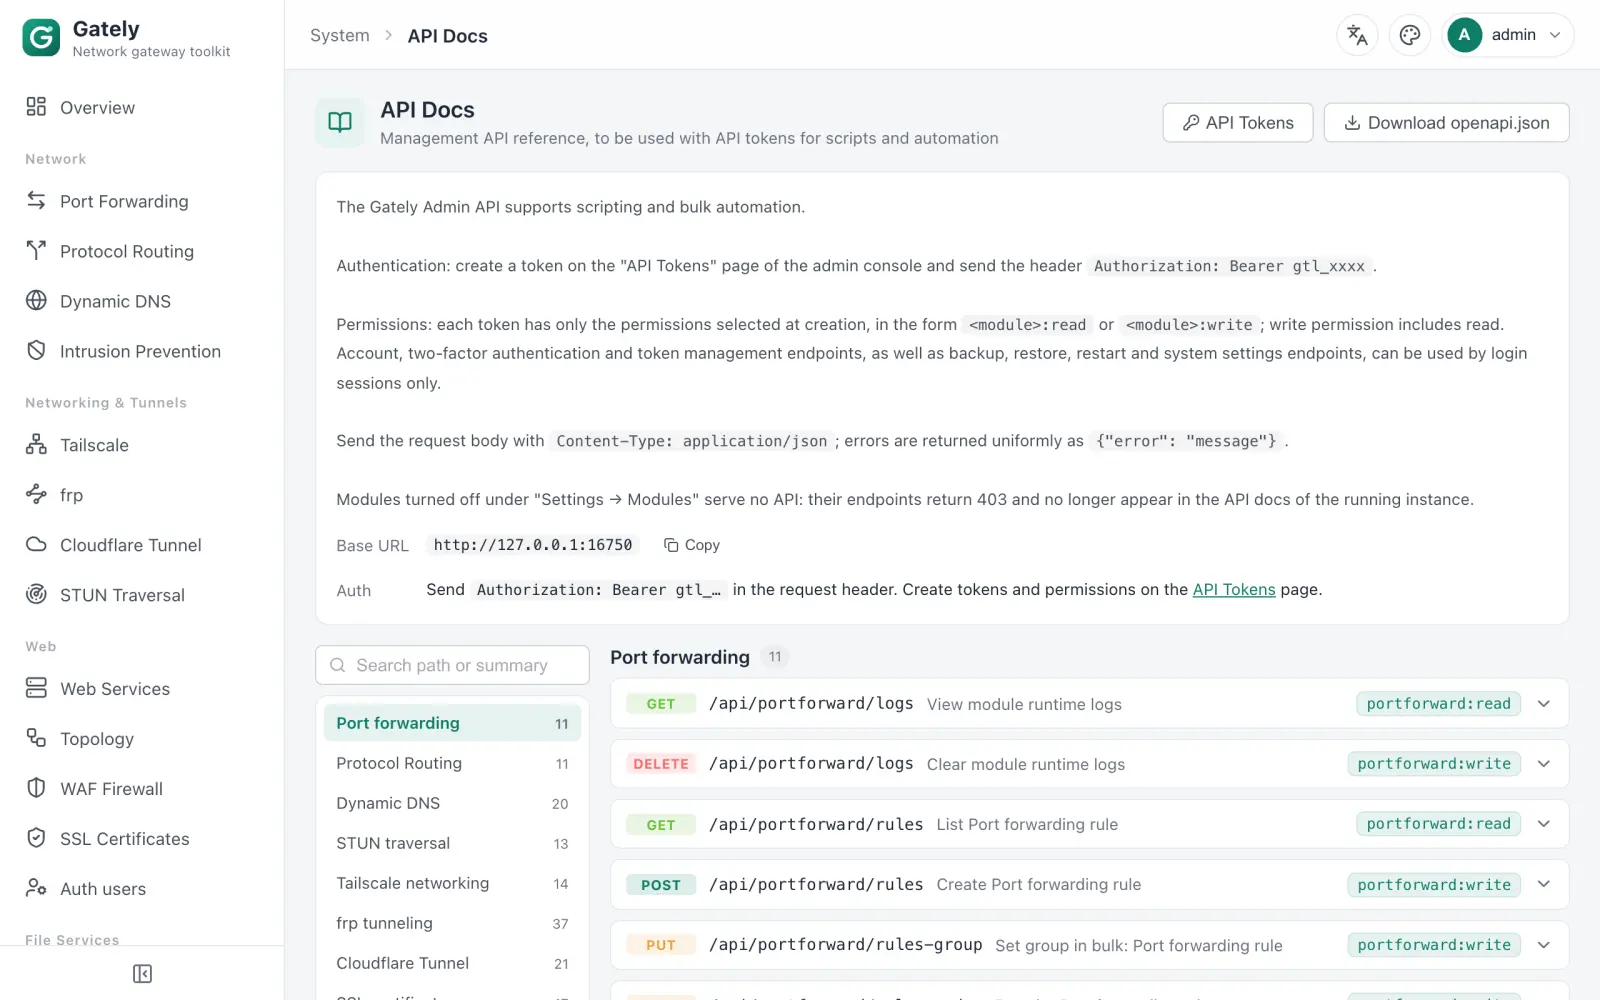
The admin UI runs on the same REST API. Tokens are scoped per module, with OpenAPI docs, a CLI and MCP.
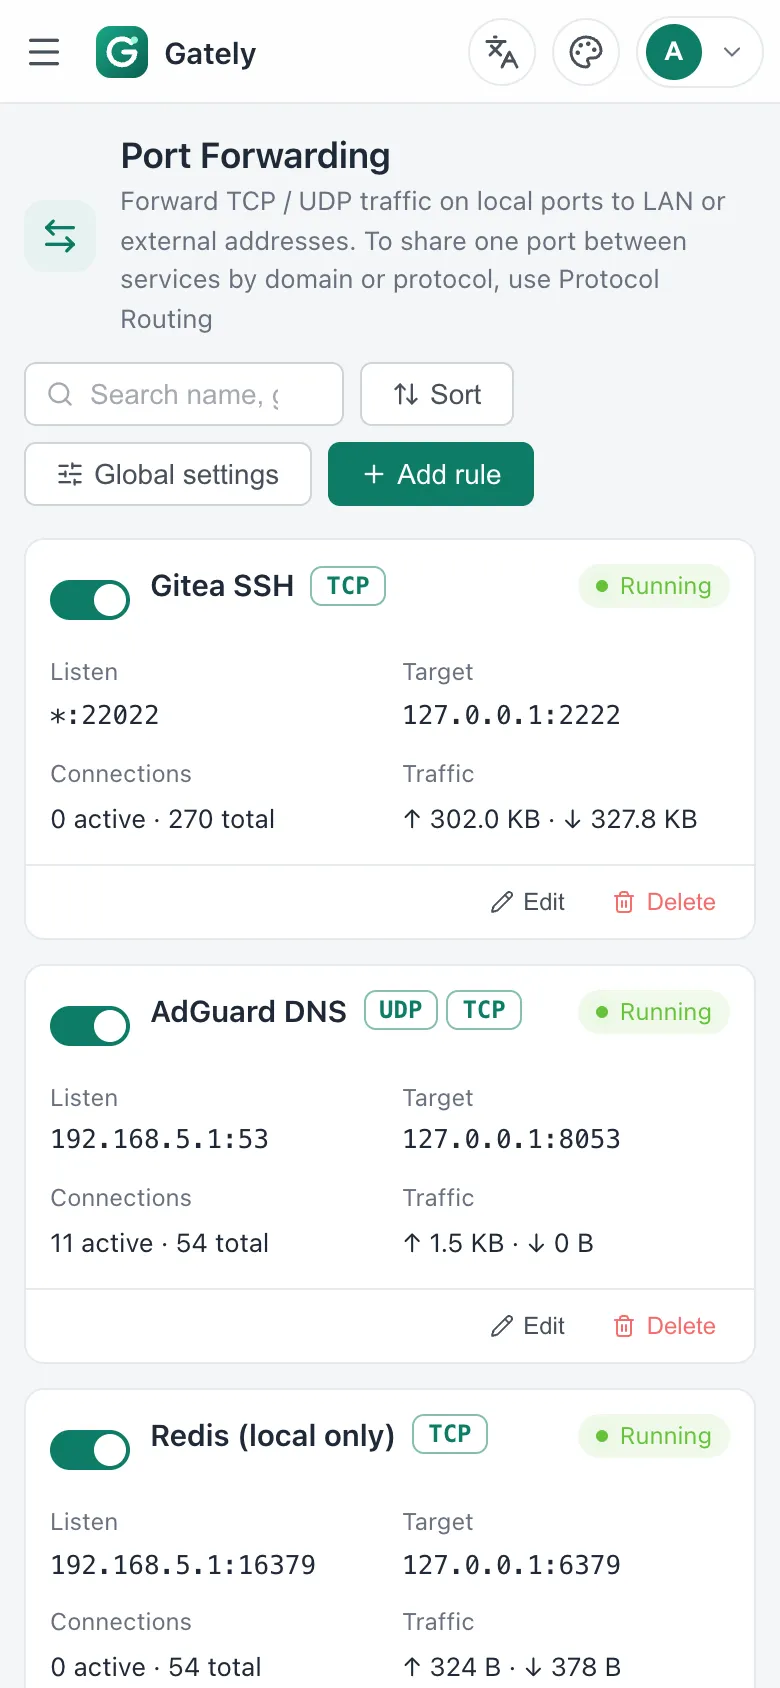
The admin UI has a dedicated phone layout, so you can check status and change settings on the go.
One command or one package gets it running, and everything is set up in the browser.
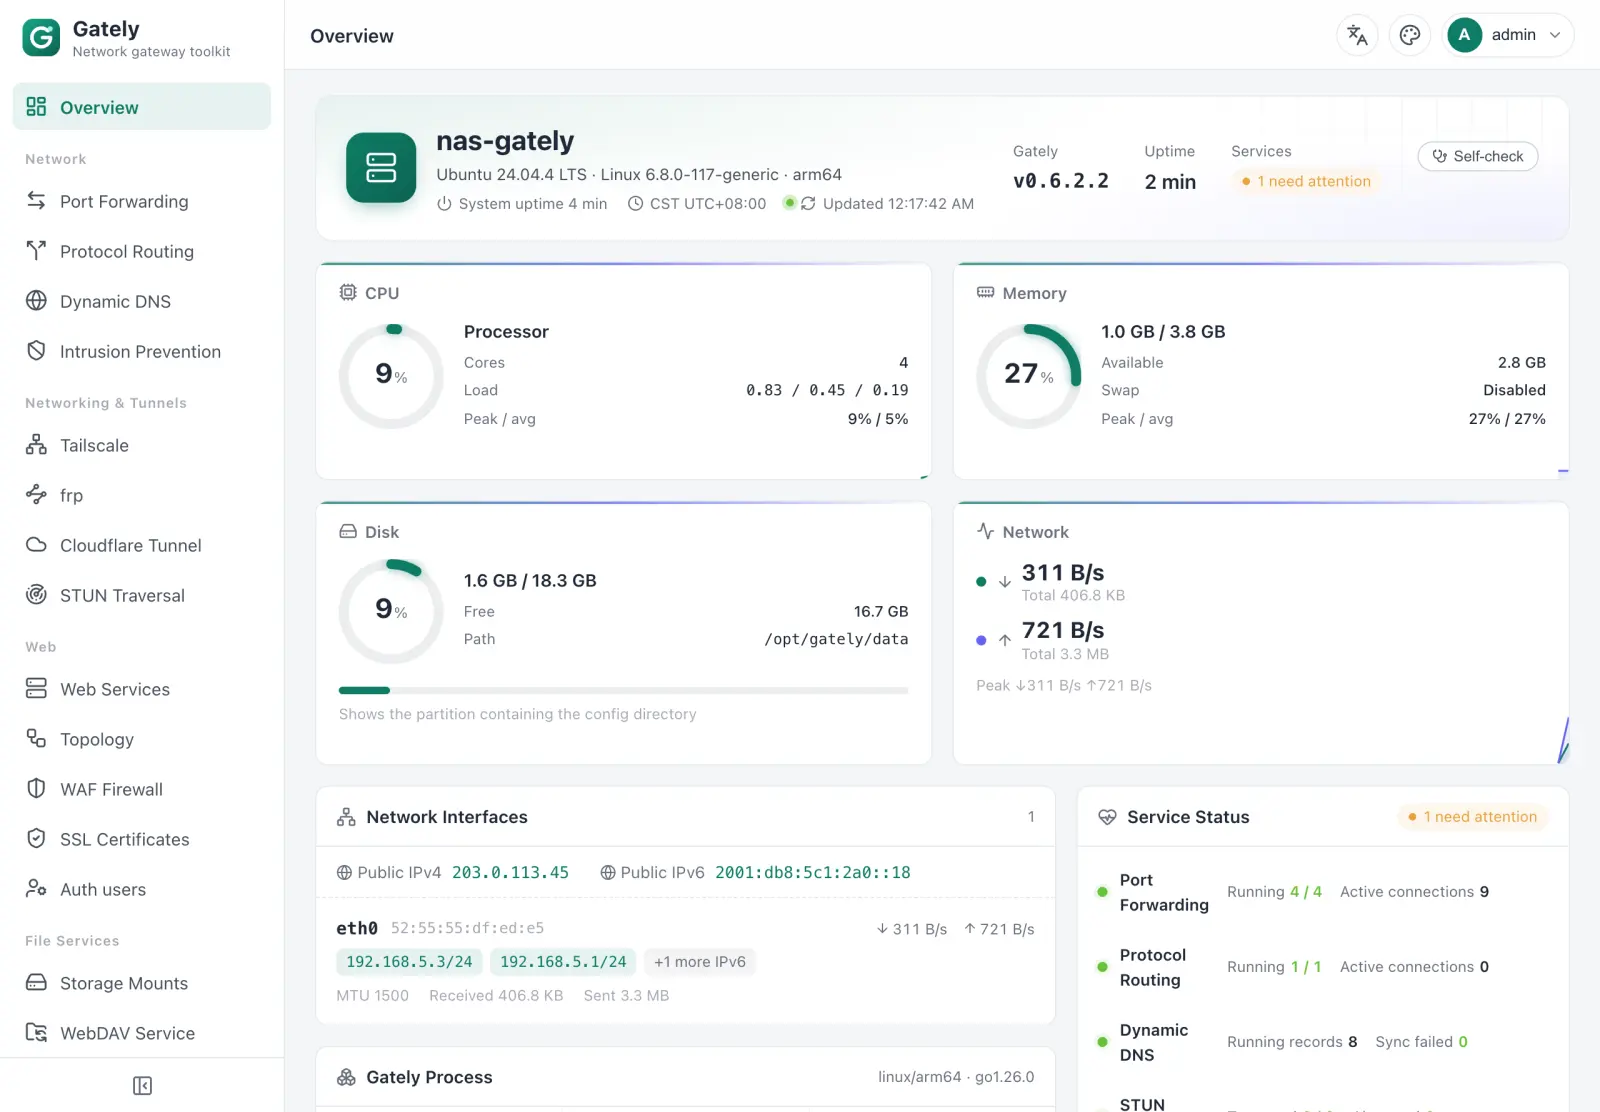
The overview shows host resources, network interfaces and public addresses, plus the state of every module, so you know at once what needs attention.
A live map of how requests travel from the Internet through listeners and sites to backends, with QPS, errors and active visitors on every node.
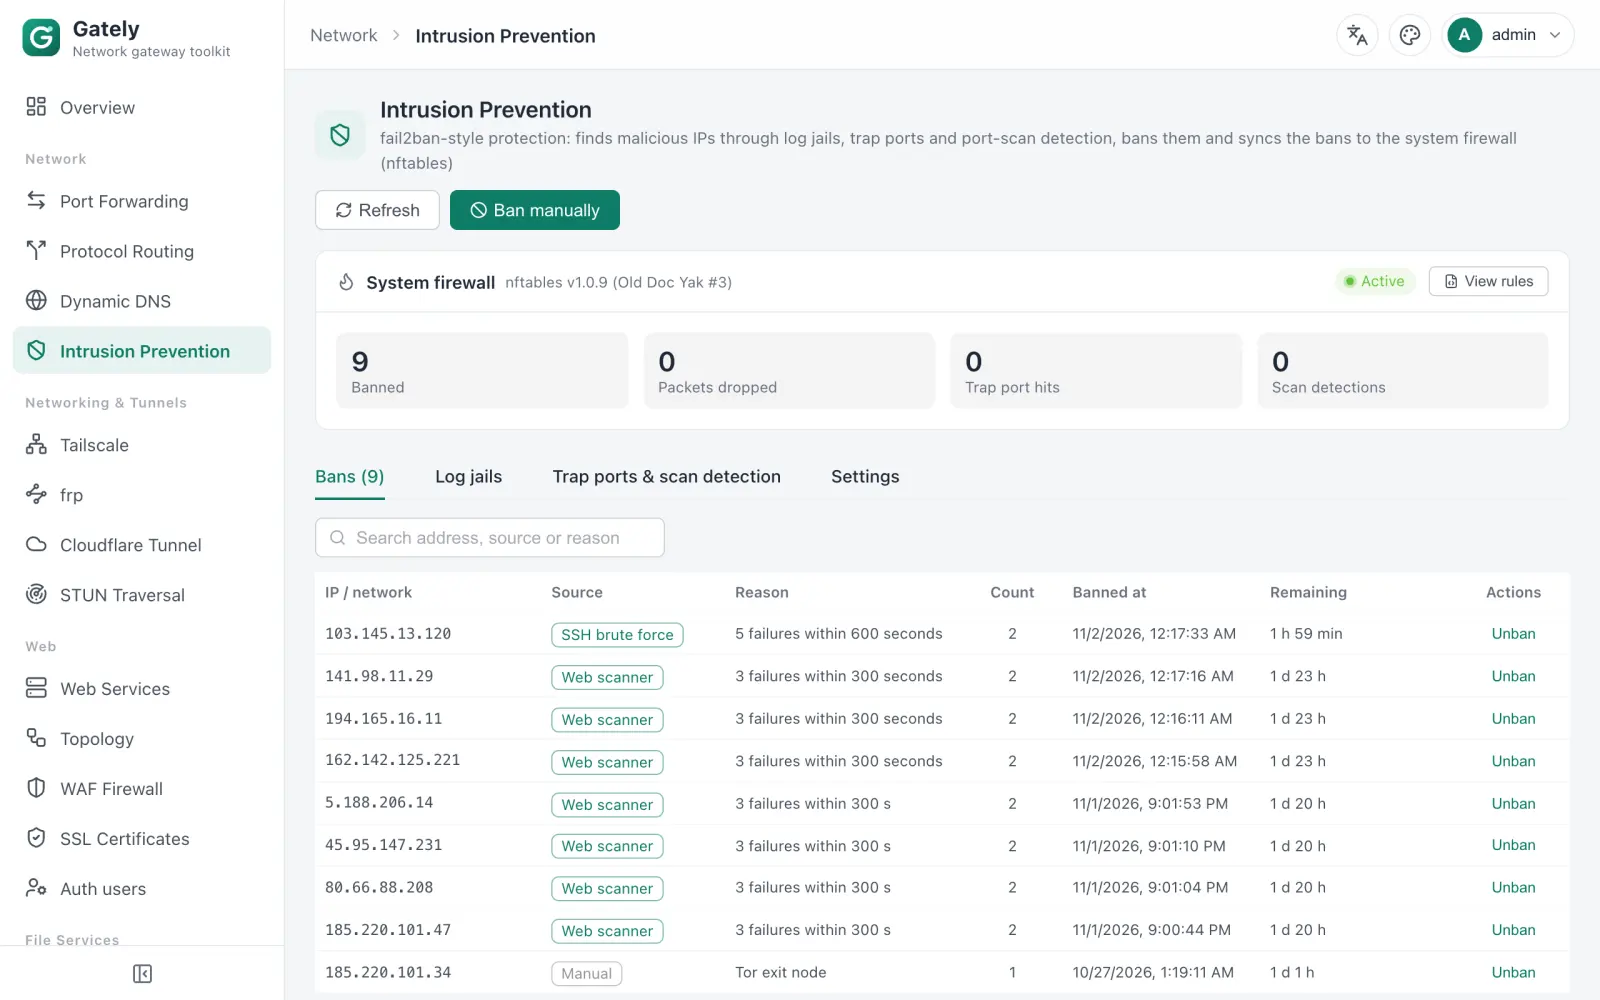
Each site can enable its own WAF, IP rules and sign-in. Intrusion prevention bans offenders from log rules and syncs them to the system firewall.
Sign-ins, config changes and access to sensitive content go into the audit log. Overwritten config files keep their previous versions, with a diff and one-click rollback.
The admin UI itself is built on the REST API. Tokens get read-only or read-write access per module, and the built-in OpenAPI docs make scripting easy.
Navigation, lists and forms are laid out again for small screens. Open the same address in your phone's browser to check status and change settings.
From pointing a domain at your home to guarding a whole row of websites, it all happens in one interface.
Major providers including Alibaba Cloud, Cloudflare, Tencent Cloud, DNSPod, Huawei Cloud, Route 53, OVH, Gandi and Namecheap; detect your IP by URL, network interface or command, IPv4 and IPv6, webhook notifications.
TCP / UDP hole punching and keep-alive, UPnP / NAT-PMP, automatic port opening in the host firewall, built-in forwarding; triggers webhooks and scripts when the public address changes.
TCP / UDP, IPv4 / IPv6, port ranges, multi-target failover, connection limits and traffic statistics; can send the PROXY protocol downstream to preserve the real client address.
Identifies the protocol from the first bytes of each connection so HTTPS, SSH, RDP, OpenVPN and 20 protocols in total share one port; TLS is routed by SNI and ALPN, HTTP by Host, without decrypting traffic; can send the PROXY protocol to backends.
Supervises Tailscale, NetBird, frp (frpc / frps) and cloudflared tunnels as managed processes, with online install, update, rollback and uninstall.
Offline packages for x86 and ARM, installed manually from the App Center. Open it from the fnOS desktop through the fnOS unified gateway, and administrators already signed in to fnOS go straight in.
Click the icon on the fnOS desktop and the admin UI opens under /app/gately/. Both the LAN address and your remote fnOS domain work, with no extra port to open or forward, and fnOS handles access control.
Turn on Sign in with fnOS and administrators already signed in to fnOS go straight into Gately, without a password or two-step code. Regular fnOS users still sign in. Off by default.
Runs as root, so it can listen on 80/443, manage Docker and open the Web terminal. Config is kept on uninstall, and upgrading is installing the newer .fpk.
Images are available for amd64, arm64 and arm/v7. After starting, open http://DEVICE_IP:16680 and sign in with the default account admin and default password gately.cn, then change the password right away.
docker run -d --name gately --network host \
  -v ./gately-data:/etc/gately \
  -v /var/run/docker.sock:/var/run/docker.sock \
ghcr.io/wangwanjie/gately:latestNo. Gately does not connect to any project servers and reports nothing; by default it anonymously checks GitHub for new releases and security advisories, which can be turned off.
Home NAS, soft routers, cloud hosts and servers of all kinds. Binaries are provided for Linux (amd64 / arm64 / arm / mips / mipsle / riscv64), macOS, Windows and FreeBSD, plus Docker images for amd64 / arm64 / arm/v7, a native app package for fnOS, and OpenWrt packages (.ipk / .apk).
Yes. Every release ships offline fnOS packages (.fpk) that you install manually from the App Center. Gately plugs into the fnOS unified gateway, so it opens from the desktop icon and also works over your remote fnOS domain. Turn on Sign in with fnOS under Settings → Access control and fnOS administrators who are signed in go straight in, without a password or two-step code.
These modules listen directly on host ports. If you do not need Docker management, you can drop the docker.sock mount.
Free, open source and ready once installed. Questions? Find us in the Telegram group.
 Scan with your phone to join the Telegram group